

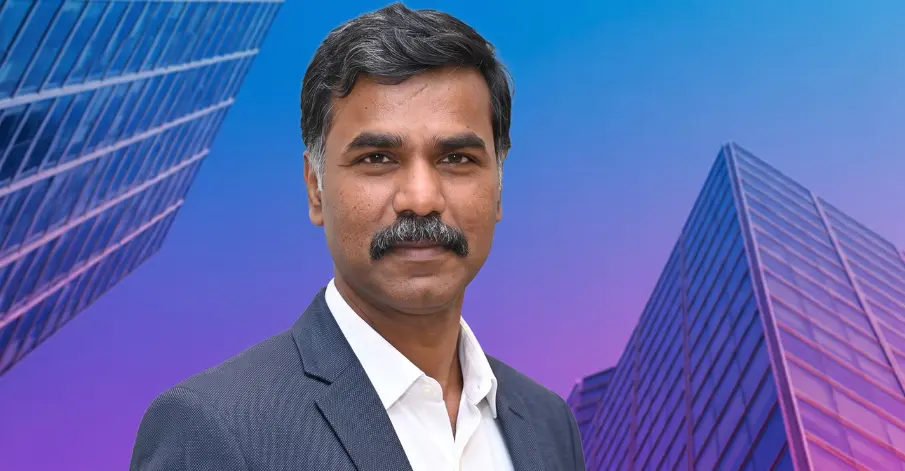
Chandrashekar Chettiar, a cybersecurity leader with more than two decades of experience across BFSI and critical infrastructure, has taken up a new role as India Region Chief Information Security Officer (CISO) at Saint-Gobain Group in India. He announced the move on LinkedIn on 17 October. The role is based in Mumbai and follows a hybrid working model.
Chettiar joins from Motilal Oswal Financial Services Ltd, where he served as CISO from September 2022 to May 2026. There, he led group-wide cybersecurity governance across multiple business entities in a regulated financial environment. He built an integrated governance, risk and compliance framework aligned with SEBI, RBI and IRDAI requirements, along with NIST and ISO standards. He reports 100% regulatory audit clearance and on-time closure of all VAPT findings with no regulatory penalties. He also led DPDP Act, 2023 gap assessments and launched enterprise data governance programmes, which he says put the organisation 12 to 18 months ahead of regulatory mandates.
His earlier stint at Tata Power, where he was Enterprise Information Security Officer from November 2018 to September 2022, is particularly relevant to his new industrial brief. He led cybersecurity across both IT and operational technology environments supporting power operations. He set up a centralised SOC covering IT and OT, which he says improved threat detection and reduced response times, and delivered ISO 27001 certification across both networks. He also served as the cybersecurity point of contact on large OT transmission refresh programmes.
Before that, he was CISO at IIFL Holdings from 2015 to 2018 and held security roles at Avanse Financial Services, L&T Finance and Essar. At L&T Finance, he built the information security function from scratch. His career began in 2001 in networking and system administration roles.
The appointment comes as industrial and manufacturing groups face growing pressure to secure connected plants alongside corporate IT, while data protection rules tighten under the DPDP Act. A leader who has handled BFSI regulation as well as IT and OT security at a power utility brings both strands to the job. Saint-Gobain has not yet shared details of his specific mandate.

 at Saint-Gobain Group in India)