

𝑶𝒓𝒈𝒂𝒏𝒊𝒛𝒂𝒕𝒊𝒐𝒏𝒔 𝒓𝒂𝒓𝒆𝒍𝒚 𝒇𝒂𝒊𝒍 𝒃𝒆𝒄𝒂𝒖𝒔𝒆 𝒕𝒉𝒆𝒚 𝒊𝒈𝒏𝒐𝒓𝒆 𝒔𝒆𝒄𝒖𝒓𝒊𝒕𝒚. They fail because they misallocate security investment across prevention and resilience.
Global cyber risk is no longer theoretical. According to multiple industry estimates, cybercrime is expected to cost the world over $10 trillion annually by 2025, and yet most enterprises still structure security budgets around legacy thinking “stop everything” or “recover later.”
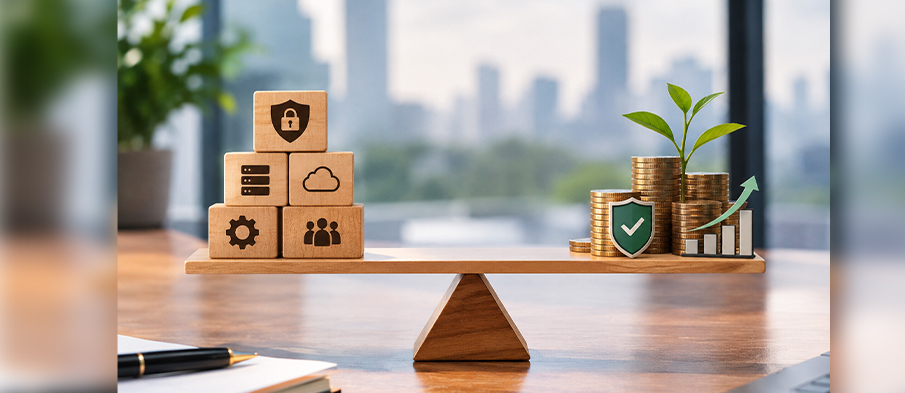
That’s the core tension: prevention vs resilience .
▸ Prevention reduces the probability of incidents
▸ Resilience reduces the impact when incidents occur
But both follow diminishing returns. And this is where most strategies break.
Over-investing in prevention leads to complex control layers tool sprawl, alert fatigue, and rigid architectures. Security looks strong on paper, but when something breaks through (and it eventually does), recovery is slow because resilience was never built in proportion.
On the other side, over-indexing on resilience creates operational acceptance of failure. Incidents become frequent, and the organization effectively pays a continuous “breach tax” through downtime, recovery costs, and reputational erosion.
The World Economic Forum has consistently highlighted that human error and system misconfigurations account for a significant share of breaches, which means purely defensive investments will never eliminate systemic risk.
This is why mature CISOs are shifting the model entirely. They treat security as a portfolio allocation problem, not a control checklist.
They optimize across three layers:
▸ Probability reduction (Prevention)
Identity security, vulnerability management, secure by design architecture, threat intelligence.
▸ Blast-radius control (Containment)
Zero Trust principles, micro-segmentation, least privilege, isolation of critical systems.
▸ Recovery velocity (Resilience)
Incident response readiness, immutable backups, failover architecture, and tested disaster recovery cycles.
My leadership POV:
The biggest shift I’ve seen is this security maturity is not defined by how few incidents you have, but by how quickly your organization returns to full operational capacity when an incident occurs.
That changes everything.
Because at scale, eliminating every risk becomes economically inefficient. The marginal cost of preventing the “last 10% of risk” often exceeds the expected business impact of that risk itself.
So the real question is not “How do we prevent breaches?”
It becomes:
“What is the optimal balance between prevention, containment, and recovery that keeps the business continuously operational under stress?”
The most effective CISOs today think like risk portfolio managers, not control enforcers.
Security is no longer about building systems that don’t fail.
It is about building systems that fail safely and recover fast enough that the business never stops moving.