

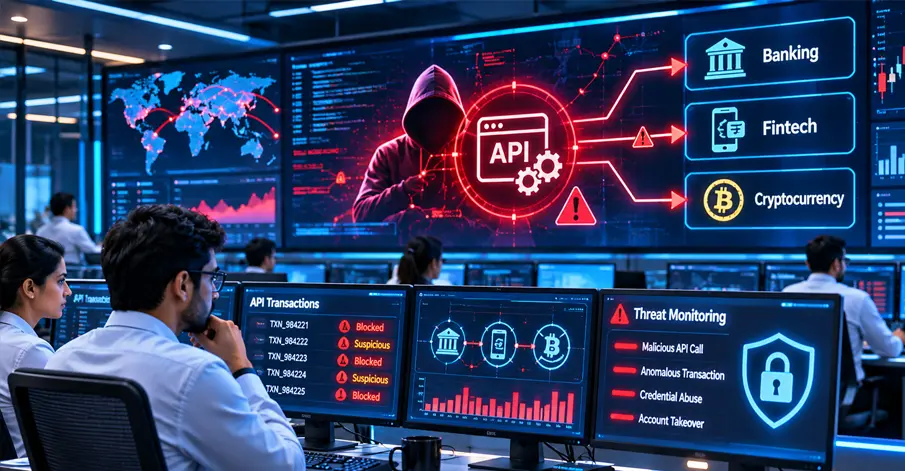
India’s Computer Emergency Response Team has warned financial-sector organisations about an active campaign identified as CRAFTY FALCON, which uses machine intelligence and publicly available AI-assisted security tools to target NBFCs, digital lenders, payment aggregators, fintech companies and cryptocurrency businesses.
The attackers have abused merchant-settlement and disbursement APIs to initiate unauthorised transfers. In some cases, they first executed small transactions, including transfers as low as ₹1, before attempting larger movements of funds. Cryptocurrency platforms were targeted through stolen wallet keys, enabling assets to be transferred from compromised wallets.
CERT-In has characterised the activity as an immediate and continuing threat. The campaign has reportedly returned to organisations after earlier remediation efforts, indicating that closing a single entry point may not remove compromised credentials, persistent access or weaknesses elsewhere in the payment workflow.
The reported use of AI does not replace conventional intrusion methods. Instead, automated systems can accelerate reconnaissance, credential testing, phishing development, vulnerability discovery and the chaining of separate weaknesses. Financial organisations remain exposed through APIs, cloud credentials, administrator accounts, third-party integrations and inadequately segmented payment systems.
The advisory places particular attention on periods of reduced monitoring, when autonomous tools can perform high-volume actions before security teams intervene. This changes the operational requirements for financial-sector security centres: transaction monitoring, API telemetry and identity controls must function continuously rather than depending on manual review during business hours.
The campaign also demonstrates why application-security and fraud-monitoring teams cannot operate independently. An attacker who gains technical access to an API may produce activity that resembles a legitimate settlement or disbursement request. Security controls therefore need to connect identity, device, behavioural and transaction signals while retaining the ability to suspend high-risk activity.
Affected organisations are expected to review settlement APIs, wallet-key storage, authentication records and privileged access; rotate exposed credentials; examine small-value precursor transactions; and preserve logs for forensic review. Firms that have already applied fixes must also check whether the attackers established new accounts, tokens or persistence mechanisms before the remediation.
The warning was issued on 4 November, but the threat remains active and was highlighted again in fresh reporting on 6 November.